Information Security
The HIS Group thoroughly enforces security measures that ensure confidentiality, integrity, and availability to protect the information assets handled by the Company. Based on our Information Security Basic Policy, we promote the reinforcement of security and strive to protect information assets, driving this initiative across the entire Group.
Basic Policy
Structure
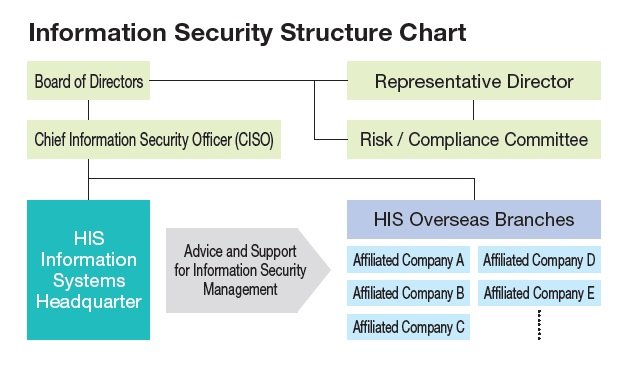
To ensure information security, we have established organizational and technical management structures to prevent unauthorized access and information leakage. Furthermore, we have constructed a management structure centered on the Chief Information Security Officer (CISO) and established an organization specializing in security measures. By coordinating various measures across the
entire Group, we have realized a more robust structure.
Measures
We utilize the latest technologies, such as IT asset management tools and EDR (Endpoint Detection and Response), to respond to increasingly sophisticated cyberattacks.
Additionally, we have established a SOC (Security Operation Center) where security analysts perform monitoring. Furthermore, we evolve our security measures by utilizing the CSF (Cyber Security Framework) of the National Institute of Standards and Technology (NIST) and the CIS Controls of the Center for Internet Security (CIS) in the United States to periodically review our countermeasure details.
Threat and Attack Monitoring
We monitor log data collected from PCs and servers, maintaining a structure to discover signs of suspicious communication or malware infections at an early stage. We also collect the latest vulnerability information and attack methods from security organizations and vendors to respond swiftly. Furthermore, by utilizing SIEM (Security Information and Event Management) to conduct log correlation analysis, we aim for the early detection of increasingly complex attacks.
Security Diagnosis
Leaving system vulnerabilities unaddressed becomes a factor that increases the risk of attacks on networks and systems. In our Company, internal security engineers conduct thorough vulnerability diagnoses and swiftly issue improvement instructions for any discovered problems. We continue our initiatives to minimize security risks by continuously conducting diagnoses and countermeasures even after releases.
Security Education
To ensure all employees recognize the importance of information security, we actively deploy educational activities and thoroughly enforce the appropriate handling of information assets.
We have established and communicated "Security Manners"--the basic security rules that must be followed--while conducting security training and confirmation tests to improve employee knowledge. Through these efforts, we enhance the IT security awareness of each and every employee and promote the thorough protection of personal information.
Continuous Improvement
To respond to the advancement of digital technology and the increasing sophistication of cyberattacks, our Company continues to reinforce security through the introduction of the latest technologies, employee education, and the development of specialists. In addition, we periodically evaluate the rationality of our information security measures, conducting reviews and improvements to always maintain an optimal security structure.
Supply Chain Security Management
For the purpose of investigating the information management structures of business partners and
contractors, we introduce security evaluations conducted by third-party organizations as necessary.